Cybersecurity Guidance
It usually starts with a document somebody sent you, or with something that already went wrong. We review your security controls, explain the gaps in plain terms, and help you answer the questionnaire accurately.
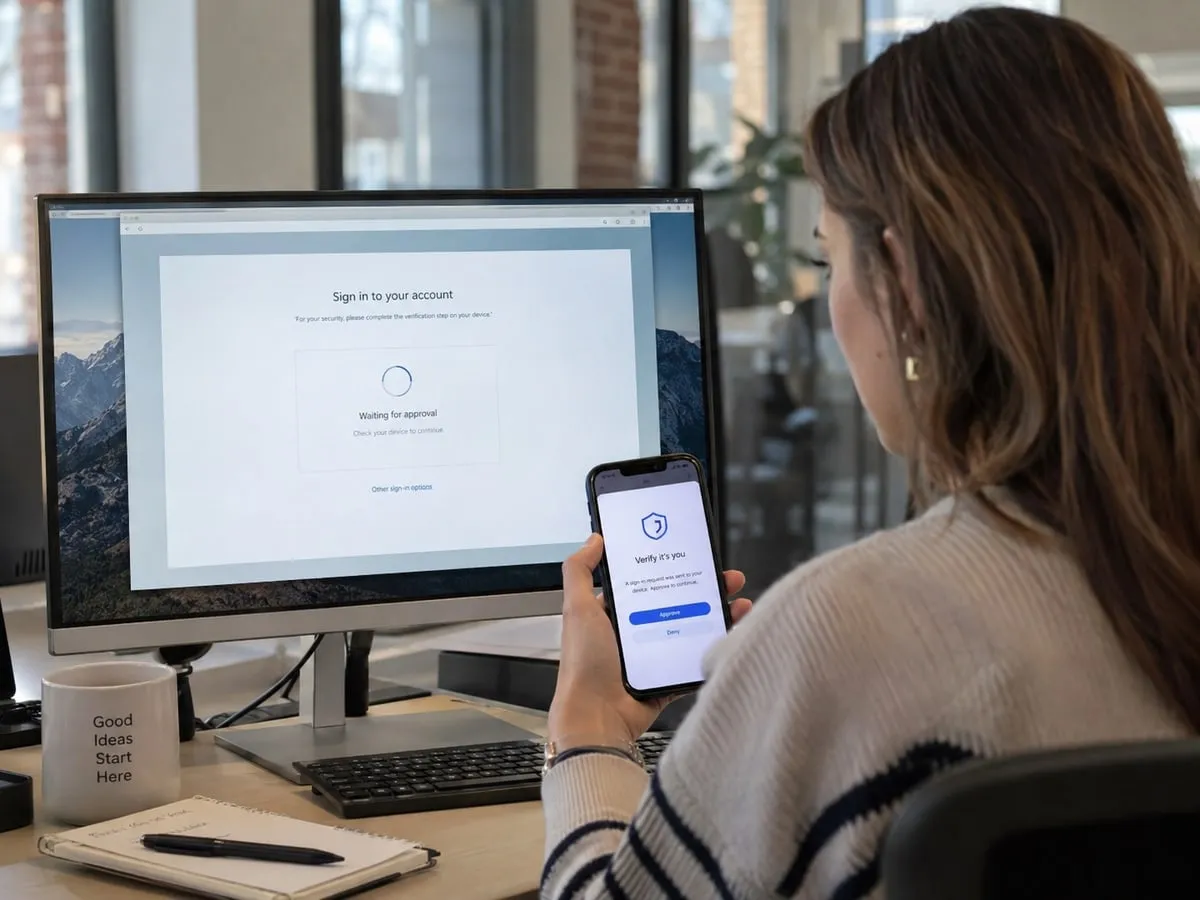
Sign-in is usually the first thing worth fixing, and it comes up on most of these forms.
- A cyber insurance form needs completing
- A suspicious link or attachment was opened
- A customer or contract asks about security controls
What the documents are asking for
None of them want a security philosophy. They want specific answers about controls you either have or do not, and the questions tend to repeat:
- A general contractor’s prequalification packet asks who can reach the drawings, what happens when a device leaves a site, and whether access is removed when someone leaves.
- A cyber insurance renewal asks about MFA on email and remote access, backups that have been restored from, and separated admin accounts. A wrong answer on an application can become a coverage problem later.
- A customer’s vendor review covers much the same ground before you are onboarded as a supplier.
We go through the form with you, check what is actually in place, and write answers you can stand behind.
After the assessment, we can scope and quote the changes you choose to move forward with. Implementation is not included in the assessment fee.
Where to start
You do not have to do all of it at once. Sign-in is usually first: everyone on MFA, no shared logins, and an admin account kept separate from the one you read mail with.
Second, make sure you can get your data back — not that backups are running, but that someone has restored from one recently enough to know it works.
Device protection, mail filtering and a written policy all matter, and they are easier to judge once those first two are settled.
| What the form asks | An example answer |
|---|---|
MFA on email and remote access | Yes |
Backups restored from, not just run | Yes |
Admin accounts kept separate | Yes |
Access removed when staff leave | Not sure |
- A written assessment of the current state
- Findings ranked by exposure, not by product
- The questionnaire in front of you, worked through answer by answer
- Verifying what is actually in place, so the answers hold up
- A remediation order with rough effort per item
- A penetration test or red-team engagement
- A formal SOC 2 or HIPAA certification audit
- 24/7 monitored incident response
- Legal advice on breach notification
Tell us what is going on.
A rough description is enough to start. We reply within one business day.